Your AI policy is useless if nobody can apply it mid-workflow
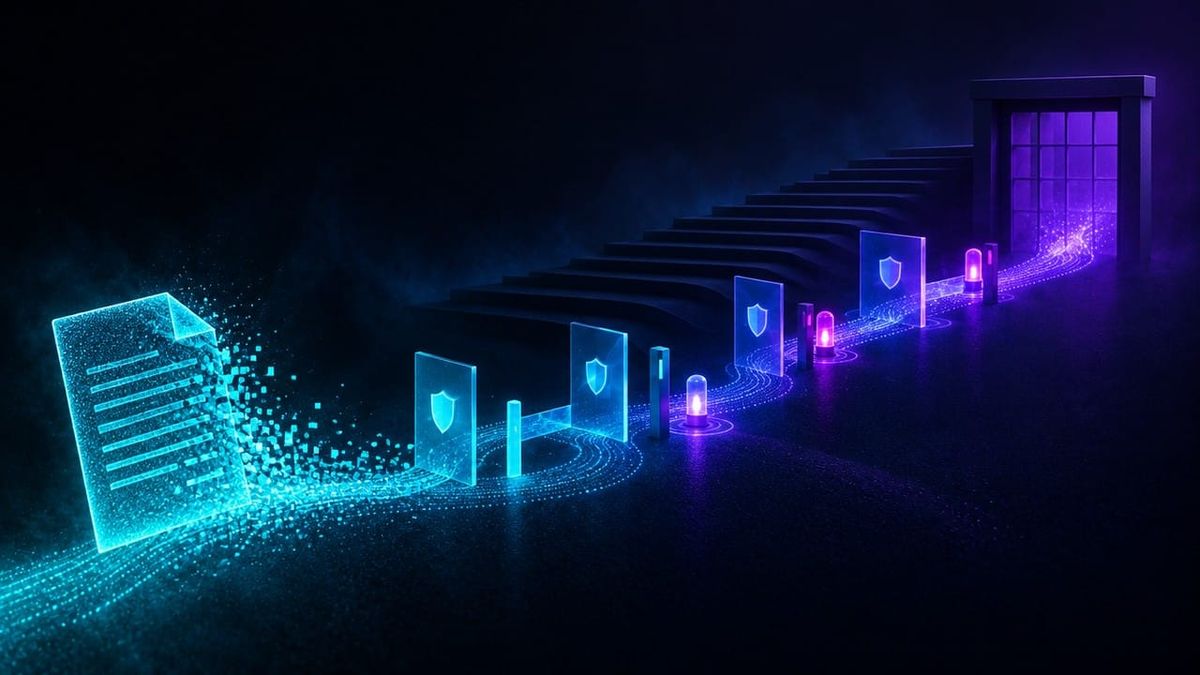
Paper policy is not governance; rules must show up as permissions, approvals and stops during the work.
Paper policy is not governance; rules must show up as permissions, approvals and stops during the work.
The policy everyone nodded at and nobody could use
The document was thorough.
It covered acceptable use, customer data, approvals, model choice and escalation. Leadership signed off. It lived in a drive folder. Staff were told to follow it.
Then a live workflow asked someone to decide in thirty seconds: send or not, write or not, escalate or guess. The policy was not in the queue. The permission model did not encode it. The stop conditions were not wired. So people improvised, and the PDF stayed pristine.
That is how businesses end up with AI governance theatre: strong language, weak runtime.
Reframe: policy only counts when it can interrupt the work
A useful AI policy is not mainly a reading exercise. It is a set of enforceable rules that appear as permissions, approval requirements, blocked actions and clear stops while work is happening.
If the rule cannot be applied at the moment of risk, it is advice. Advice helps when people have time and calm. Live AI workflows often offer neither.
So the standard should not be, “Do we have an AI policy?” The standard should be, “Can a competent operator apply the relevant rule mid-workflow without leaving the tool to go hunting for a PDF?”
If the answer is no, you have documentation. You do not yet have governance.
What breaks when policy stays outside the workflow
People invent local rules. Under time pressure, teams create shortcuts. Those shortcuts become the real policy, undocumented and uneven.
Approvals ignore the written standard. The queue asks for yes/no. The policy asked for context, dual control or a customer-status check. Only the queue is visible, so only the queue is followed.
Incidents become “training issues”. After a miss, leaders point to the unread paragraph. The deeper miss was design: the rule never had a runtime handle.
Audits look better than operations feel. The binder is complete. The customer experience still shows unmanaged AI behaviour.
The deeper issue is confusing intent with control. Intent belongs in policy. Control belongs in the path the work actually takes.
Practical standards for enforceable mid-workflow rules
1. Translate policy clauses into runtime controls
For each consequential rule, name the control: permission, approval, block, warning, or mandatory field. If you cannot name the control, the clause is not ready for production AI.
2. Put the rule where the decision happens
Customer-send rules belong on the send gate. Permanent-record rules belong on the write gate. Access rules belong on the connector and role. Do not rely on a monthly reminder to do the job of a stop.
3. Make stops obvious and recoverable
When a rule fires, show why, what is blocked, and how to escalate or fix. Silent failure and cryptic errors teach people to bypass controls.
4. Keep the operator-facing text short
Runtime guidance should be readable in a hurry. Link to the full policy for depth, but do not require a full read to make a safe live decision.
5. Review controls when workflows change
A new connector, model, or agent role can bypass an old control path. Policy reviews that ignore runtime maps drift into irrelevance quickly.
Five questions before you trust your AI policy
- Which policy rules are consequential enough to need a runtime control?
- Where does each rule appear in the live workflow?
- What happens when the rule blocks work — stop, escalate, or workaround?
- Who can change the control, and how is that change recorded?
- How do incidents update both the policy text and the runtime rule?
If those answers are fuzzy, fix the workflow hooks before you write another polished paragraph.
I treat this as operating design. Governance is what the system does under pressure, not what the binder says on a quiet afternoon.
A short rule in the right place beats a long rule nowhere
Operators do not fail policies because they dislike governance. They fail policies because the live moment offers no handle. A one-line stop on the send gate outperforms a five-page chapter that never appears when the button is clicked.
When you rewrite policy, ask for each clause: where does this interrupt the work? If you cannot point to a screen, permission or approval card, keep writing until you can.
At Walter, I am focused on helping businesses run AI work with clearer ownership, shared context and visible hand-offs. Enforceable mid-workflow rules are how policy becomes part of that system.
A useful assistant can follow instructions. A trustworthy operating layer makes the important instructions unavoidable: permissions, approvals and stops at the moment of risk.
Speed still matters. Encode the few rules that prevent expensive harm, and keep them visible in the path of work. Teams move faster when they are not forced to choose between policy and getting the job done.
If your AI policy only lives in a document, wire it into the workflow before you scale automation.
Translate clauses into controls. Place them on the decision. Make stops clear. Keep operator text short. Review runtime maps when tools change. Update controls when incidents teach you something.
Do that, and AI policy becomes usable governance rather than unread reassurance.
Join the waitlist at https://hirewalter.ai/